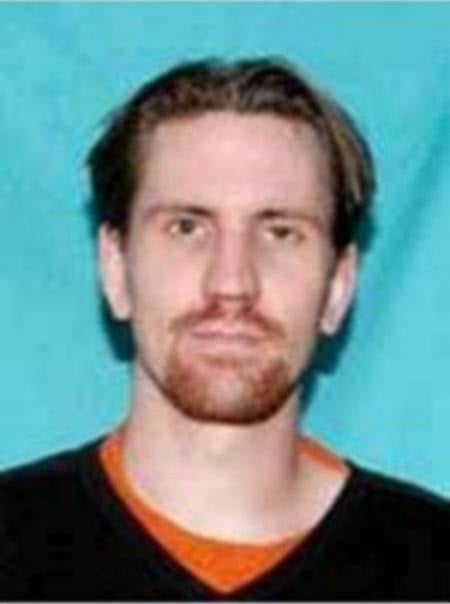
The person at the center of this case
Bjorn Daniel Sundin (fugitive defendant)
Cold Case · Open - Fugitive at Large
16 years waiting · since 2010
BJORN DANIEL SUNDIN
Justice for Bjorn Daniel Sundin (fugitive defendant) — the trail went cold in 2010, but the truth hasn't.
Start here
Key leads to think about
🎯
suspect
Lead #1Where is Sundin currently located given his known ties to Sweden and Ukraine?
🔍
evidence
Lead #2What bank accounts in Europe received the fraudulent proceeds and can they be traced?
👤
person
Lead #3Who are all the co-conspirators and call center representatives involved in the scheme?
Bjorn Daniel Sundin is wanted for his role in a massive international cybercrime scheme operating from December 2006 to October 2008 that defrauded over one million internet users across 60+ countries of more than $100 million through fake "scareware" software. Using browser hijacking, fraudulent error messages, and deceptive advertisements on legitimate websites, Sundin and co-conspirators tricked victims into purchasing worthless software products while call center staff were instructed to lie to prevent fraud reports. He was indicted in Chicago on May 26, 2010, and remains at large with known ties to Sweden and Ukraine.
Case
#638
United States District Court, Northern District of Illinois; Federal Bureau of Investigation
Try asking
Claim this imported case
A one-time $10 claim transfers this imported case workspace to your account. You get 10 uploads for this case, 25 daily AI questions for this case, and public tips with files route to you.
10 uploads25 AI questions/day
This does not start a subscription. When the included limits are reached, the Personal plan unlocks more workspace capacity.
More leads to consider
Beyond the top three above — each detail below could be the thread that pulls this case open.
💡
clue
Lead #4How were fake advertisements placed on legitimate companies' websites and which companies were exploited?
⏰
timeline
Lead #5Why did the operation suddenly cease in October 2008 and what triggered the May 2010 indictment?
Have information about any of these leads?
Even the smallest detail could be the key to solving this case.
Official wording
Source Narrative
Wire Fraud; Conspiracy to Commit Computer Fraud; Computer Fraud Caution: Bjorn Daniel Sundin, along with his co-conspirator, Shaileshkumar P. Jain , is wanted for his alleged involvement in an international cybercrime scheme that caused internet users in more than 60 countries to purchase more than one million bogus software products, resulting in consumer loss of more than $100 million.
It is alleged that from December 2006 to October 2008, through fake advertisements placed on legitimate companies’ websites, Sundin and his accomplices deceived internet users into believing that their computers were infected with “malware” or had other critical errors in order to encourage them to purchase “scareware” software products that had limited or no ability to remedy the purported defects. Sundin and his co-conspirators allegedly deceived victims, through browser hijacking, multiple fraudulent scans and false error messages, into purchasing full paid versions of software products offered by their company, Innovative Marketing, Inc.
The proceeds of these credit card sales were allegedly deposited into bank accounts controlled by the defendant and others around the world, and were then transferred to bank accounts located in Europe. When customers complained that their purchases were actually fraudulent software, call center representatives were allegedly instructed to lie or provide refunds in order to prevent fraud reports to law enforcement or credit companies.
On May 26, 2010, Sundin was indicted in Chicago, Illinois, by a federal grand jury for the United States District Court, Northern District of Illinois. He was indicted for wire fraud, conspiracy to commit computer fraud and computer fraud.
That same day, a federal warrant was issued for Sundin’s arrest. Remarks: Sundin has ties to Sweden and the Ukraine.
Timeline of Events
🕵️
2006-12-01
Scareware scheme begins
Fraudulent scareware operation allegedly begins in December 2006
🕵️
2008-10-31
Scheme concludes
Scareware operation allegedly ends in October 2008
🕵️
2010-05-26
Federal indictment
Bjorn Daniel Sundin indicted in Chicago for wire fraud, conspiracy to commit computer fraud, and computer fraud
Key Locations
Interactive map showing important locations related to this case
Case Information
Incident:December 1, 2006
Last Updated:September 11, 2026
Up to $20,000 Reward
For information leading to the resolution of this case
Leave a comment
Comments
Case Information
Incident:December 1, 2006
Last Updated:September 11, 2026
Up to $20,000 Reward
For information leading to the resolution of this case