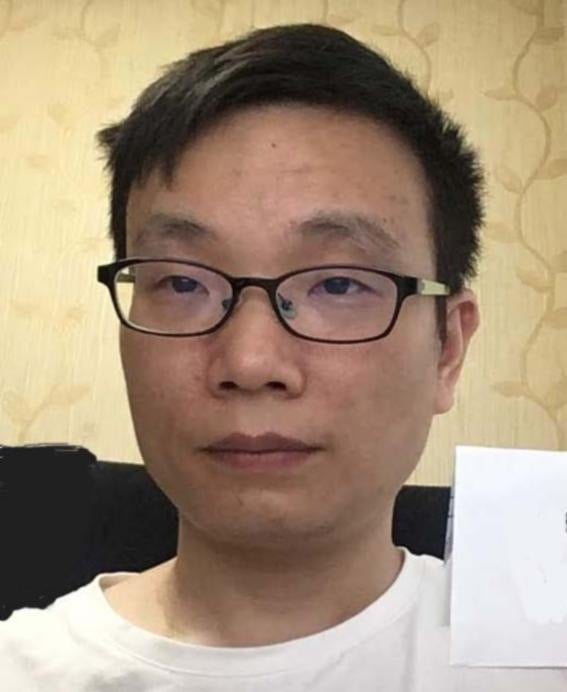
The person at the center of this case
Multiple organizations and individuals affected by cybercriminal activities
Cold Case · Open
6 years waiting · since 2020
FU QIANG
Justice for Multiple organizations and individuals affected by cybercriminal activities — the trail went cold in 2020, but the truth hasn't.
Start here
Key leads to think about
🎯
suspect
Lead #1Fu Qiang's current whereabouts and operational status within APT 41/BARIUM hacking group
🔍
evidence
Lead #2Supply chain attack methodologies and infrastructure used to compromise hundreds of companies globally
📍
location
Lead #3Identification of additional command and control servers or safe houses beyond Chengdu, China
On August 11, 2020, a federal grand jury in Washington, D.C. indicted Chinese national Fu Qiang and two co-conspirators for their roles in a sophisticated cybercriminal operation targeting hundreds of companies worldwide. Fu Qiang, employed by Chengdu 404 Network Technology Company, allegedly orchestrated supply chain attacks, ransomware deployments, and identity theft schemes affecting telecommunications, government, defense, and technology sectors across multiple continents. The case remains active as authorities work to locate and apprehend Fu Qiang, who is believed to operate from China and poses an ongoing threat to critical infrastructure and private sector networks globally.
Case
#878
Federal Bureau of Investigation (FBI); U.S. District Court for the District of Columbia
Try asking
Claim this imported case
A one-time $10 claim transfers this imported case workspace to your account. You get 10 uploads for this case, 25 daily AI questions for this case, and public tips with files route to you.
10 uploads25 AI questions/day
This does not start a subscription. When the included limits are reached, the Personal plan unlocks more workspace capacity.
More leads to consider
Beyond the top three above — each detail below could be the thread that pulls this case open.
💡
clue
Lead #4Financial flows and money laundering networks used to launder proceeds from ransomware and extortion schemes
👁️
witness
Lead #5Potential informants within Chengdu 404 Network Technology Company or affiliated cybercriminal networks
Have information about any of these leads?
Even the smallest detail could be the key to solving this case.
Official wording
Source Narrative
Racketeering Conspiracy; Conspiracy; Identity Theft; Aggravated Identity Theft; Access Device Fraud; Obtaining Information by Unauthorized Access to Protected Computers; Intentionally Causing Damage to Protected Computers; Threatening to Damage a Protected Computer; Money Laundering Caution: FU Qiang is part of a Chinese hacking group known as APT 41 and BARIUM. On August 11, 2020, a Grand Jury in the District of Columbia returned an indictment against Chinese nationals FU Qiang, JIANG Lizhi , and QIAN Chuan on multiple charges including Racketeering Conspiracy; Conspiracy; Identity Theft; Aggravated Identity Theft; Access Device Fraud; Obtaining Information by Unauthorized Access to Protected Computers; Intentionally Causing Damage to Protected Computers; Threatening to Damage a Protected Computer; and Money Laundering.
These charges stem from their alleged unauthorized computer intrusions while employed by Chengdu 404 Network Technology Company. The defendants allegedly conducted supply chain attacks to gain unauthorized access to networks throughout the world, targeting hundreds of companies representing a broad array of industries to include: social media, telecommunications, government, defense, education, and manufacturing.
These victims included companies in Australia, Brazil, Germany, India, Japan and Sweden. The defendants allegedly targeted telecommunications providers in the United States, Australia, China (Tibet), Chile, India, Indonesia, Malaysia, Pakistan, Singapore, South Korea, Taiwan, and Thailand.
The defendants allegedly deployed ransomware attacks and demanded payments from victims. Remarks: FU Qiang has ties to Chengdu, China.
Timeline of Events
🕵️
2020-08-11
Federal Grand Jury Indictment
Grand Jury in the District of Columbia returned indictment against Fu Qiang and co-conspirators on charges including racketeering conspiracy, identity theft, unauthorized computer access, and money laundering
Key Locations
Interactive map showing important locations related to this case
Case Information
Incident:August 11, 2020
Last Updated:September 10, 2026
Leave a comment
Comments
Case Information
Incident:August 11, 2020
Last Updated:September 10, 2026