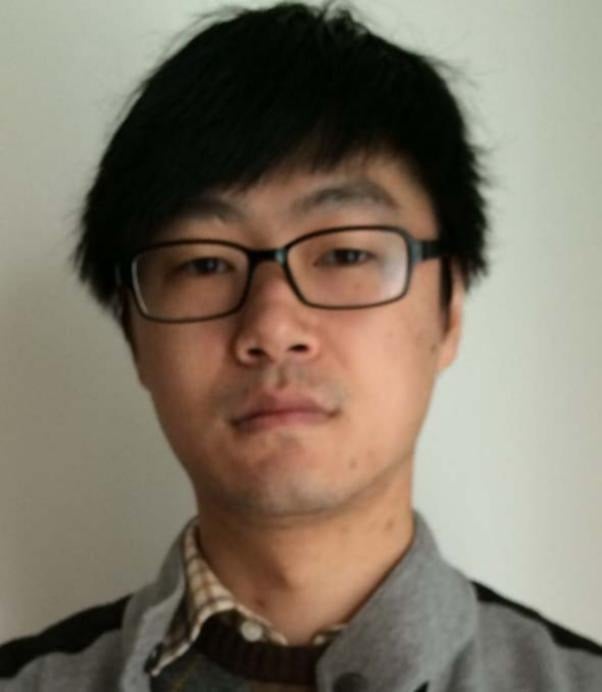
The person at the center of this case
JIANG Lizhi (Chinese national, alleged cybercriminal)
Cold Case · Open
6 years waiting · since 2020
JIANG LIZHI
Justice for JIANG Lizhi (Chinese national, alleged cybercriminal) — the trail went cold in 2020, but the truth hasn't.
Start here
Key leads to think about
🎯
suspect
Lead #1What is JIANG Lizhi's current location and how is he evading international law enforcement?
🔍
evidence
Lead #2What specific supply chain vulnerabilities did APT 41 exploit to compromise hundreds of companies globally?
📍
location
Lead #3What is the operational structure and role of Chengdu 404 Network Technology Company in coordinating these attacks?
On August 11, 2020, a federal grand jury in Washington, D.C. indicted Chinese national JIANG Lizhi, a member of the APT 41/BARIUM hacking group, for leading sophisticated cyberattacks targeting hundreds of companies across telecommunications, government, defense, and other critical sectors worldwide. JIANG and his co-conspirators, allegedly employed by Chengdu 404 Network Technology Company, conducted supply chain attacks, deployed ransomware, and stole sensitive data from victims in at least 12 countries including the United States, Australia, and India. The case remains active as authorities work to locate and apprehend JIANG, who is believed to have ties to Chengdu, China.
Case
#766
Federal Bureau of Investigation (FBI); U.S. District Court for the District of Columbia
Try asking
Claim this imported case
A one-time $10 claim transfers this imported case workspace to your account. You get 10 uploads for this case, 25 daily AI questions for this case, and public tips with files route to you.
10 uploads25 AI questions/day
This does not start a subscription. When the included limits are reached, the Personal plan unlocks more workspace capacity.
More leads to consider
Beyond the top three above — each detail below could be the thread that pulls this case open.
💡
clue
Lead #4How much money did the defendants obtain through ransomware demands and where were the proceeds laundered?
👤
person
Lead #5What are the connections between JIANG Lizhi, QIAN Chuan, and FU Qiang, and are there additional conspirators yet to be identified?
Have information about any of these leads?
Even the smallest detail could be the key to solving this case.
Official wording
Source Narrative
Racketeering Conspiracy; Conspiracy; Identity Theft; Aggravated Identity Theft; Access Device Fraud; Obtaining Information by Unauthorized Access to Protected Computers; Intentionally Causing Damage to Protected Computers; Threatening to Damage a Protected Computer; Money Laundering Caution: JIANG Lizhi is part of a Chinese hacking group known as APT 41 and BARIUM. On August 11, 2020, a Grand Jury in the District of Columbia returned an indictment against Chinese nationals JIANG Lizhi, QIAN Chuan , and FU Qiang on multiple charges including Racketeering Conspiracy; Conspiracy; Identity Theft; Aggravated Identity Theft; Access Device Fraud; Obtaining Information by Unauthorized Access to Protected Computers; Intentionally Causing Damage to Protected Computers; Threatening to Damage a Protected Computer; and Money Laundering.
These charges stem from their alleged unauthorized computer intrusions while employed by Chengdu 404 Network Technology Company. The defendants allegedly conducted supply chain attacks to gain unauthorized access to networks throughout the world, targeting hundreds of companies representing a broad array of industries to include: social media, telecommunications, government, defense, education, and manufacturing.
These victims included companies in Australia, Brazil, Germany, India, Japan and Sweden. The defendants allegedly targeted telecommunications providers in the United States, Australia, China (Tibet), Chile, India, Indonesia, Malaysia, Pakistan, Singapore, South Korea, Taiwan, and Thailand.
The defendants allegedly deployed ransomware attacks and demanded payments from victims. Remarks: JIANG Lizhi has ties to Chengdu, China.
Timeline of Events
🕵️
2020-08-11
Federal Indictment Returned
Grand Jury in the District of Columbia returned indictment against JIANG Lizhi, QIAN Chuan, and FU Qiang on charges including racketeering conspiracy, identity theft, unauthorized computer access, and money laundering
Key Locations
Interactive map showing important locations related to this case
Case Information
Incident:August 11, 2020
Last Updated:October 30, 2026
Leave a comment
Comments
Case Information
Incident:August 11, 2020
Last Updated:October 30, 2026