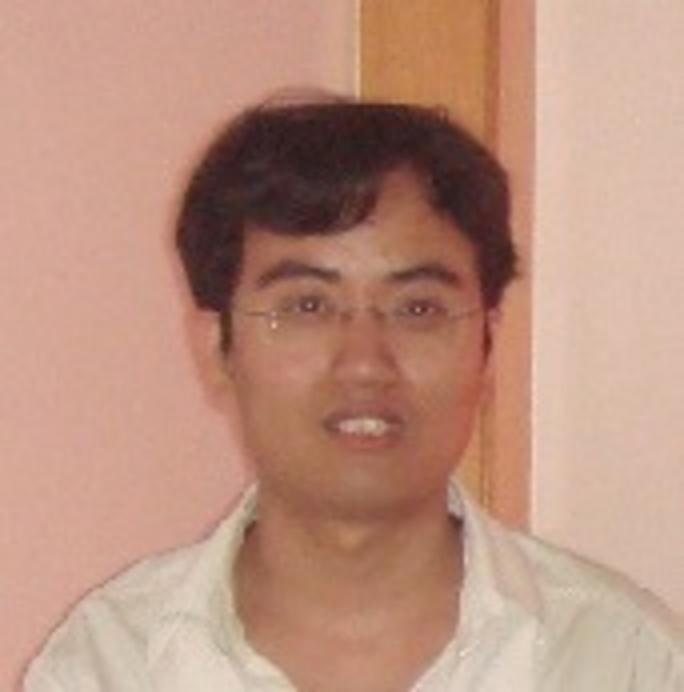
The person at the center of this case
Multiple commercial, defense technology companies, managed service providers, and U.S. government agencies; over 100,000 U.S. Navy personnel
Cold Case · Open
7 years waiting · since 2018
ZHANG SHILONG
Justice for Multiple commercial, defense technology companies, managed service providers, and U.S. government agencies; over 100,000 U.S. Navy personnel — the trail went cold in 2018, but the truth hasn't.
Start here
Key leads to think about
🎯
suspect
Lead #1Zhang Shilong (aka Baobeilong, Zhang Jianguo, Atreexp) - alleged leader of APT 10 Group operations targeting U.S. and international entities
🔍
evidence
Lead #2Compromised data from 45+ commercial and defense technology companies across aviation, space, manufacturing, oil and gas, communications, and maritime sectors
👤
person
Lead #3Zhu Hua (aka Afwar, CVNX, Alayos, Godkiller) - co-defendant and fellow APT 10 Group member
Zhang Shilong, a member of the Chinese hacking group APT 10, was indicted in December 2018 for leading a sophisticated cyber espionage campaign that compromised over 45 commercial and defense technology companies, managed service providers, and U.S. government agencies from 2006 through 2018. The operation, conducted in association with China's Ministry of State Security, targeted intellectual property and confidential information across aviation, space, manufacturing, energy, and maritime sectors, while also stealing personally identifiable information of over 100,000 U.S. Navy personnel. The case remains significant as a major international cybercrime investigation highlighting state-sponsored hacking operations and the ongoing threat to critical infrastructure and national security.
Case
#784
United States District Court for the Southern District of New York; FBI
Try asking
Claim this imported case
A one-time $10 claim transfers this imported case workspace to your account. You get 10 uploads for this case, 25 daily AI questions for this case, and public tips with files route to you.
10 uploads25 AI questions/day
This does not start a subscription. When the included limits are reached, the Personal plan unlocks more workspace capacity.
More leads to consider
Beyond the top three above — each detail below could be the thread that pulls this case open.
💡
clue
Lead #4Connection to Chinese Ministry of State Security's Tianjin State Security Bureau suggests state-sponsored cyber espionage
🔍
evidence
Lead #5Stolen personally identifiable information of 100,000+ U.S. Navy personnel and compromised U.S. Department of the Navy systems
Have information about any of these leads?
Even the smallest detail could be the key to solving this case.
Official wording
Source Narrative
Conspiracy to Commit Computer Intrusions; Conspiracy to Commit Wire Fraud; Aggravated Identity Theft Caution: On December 17, 2018, a grand jury in the United States District Court for the Southern District of New York indicted ZHANG SHILONG, aka “Baobeilong,” aka “Zhang Jianguo,” aka “Atreexp," and ZHU HUA , aka “Afwar,” aka “CVNX,” aka “Alayos,” aka “Godkiller,” two members of a hacking group operating in China known in the cybersecurity community as Advanced Persistent Threat 10 (the “ APT 10 Group ”), with conspiracy to commit computer intrusion, conspiracy to commit wire fraud, and aggravated identity theft. The defendants worked for Huaying Haitai Science and Technology Development Company located in Tianjin, China, and they acted in association with the Chinese Ministry of State Security’s Tianjin State Security Bureau.
As alleged in the Indictment, from at least 2006 through 2018, the defendants conducted extensive campaigns of global intrusions into computer systems aiming to steal, among other data, intellectual property and confidential business and technological information from more than at least 45 commercial and defense technology companies in at least a dozen states, managed service providers (“MSP”), which are companies that remotely manage the information technology infrastructure of businesses and governments around the world, and U.S. government agencies.
The victim companies targeted by ZHANG SHILONG and ZHU HUA were involved in a diverse array of commercial activity, industries, and technologies, including aviation, space and satellite technology, manufacturing technology, oil and gas exploration, production technology, communications technology, computer processor technology, and maritime technology. In addition, for example, the APT 10 Group’s campaign compromised the data of an MSP and certain of its clients located in at least 12 countries including Brazil, Canada, Finland, France, Germany, India, Japan, Sweden, Switzerland, the United Arab Emirates, the United Kingdom, and the United States.
The APT 10 group also compromised computer systems containing information regarding the United States Department of the Navy and stole the personally identifiable information of more than 100,000 Navy personnel.
Timeline of Events
🕵️
2006
Campaign begins
APT 10 Group begins extensive campaigns of global computer intrusions
🕵️
2018-12-17
Federal indictment
Grand jury in U.S. District Court for the Southern District of New York indicts Zhang Shilong and Zhu Hua on charges of conspiracy to commit computer intrusion, wire fraud, and aggravated identity theft
Key Locations
Interactive map showing important locations related to this case
Case Information
Incident:January 1, 2006
Last Updated:October 30, 2026
Leave a comment
Comments
Case Information
Incident:January 1, 2006
Last Updated:October 30, 2026